

Introduction
Modern dealership websites have become sophisticated business platforms rather than simple digital brochures. Inventory search, finance applications, service scheduling, chat tools, digital retail platforms, advertising technologies, analytics services, CRM integrations, OEM widgets, and third-party marketing tools often operate simultaneously behind the scenes. While each technology may deliver business value, together they create a complex ecosystem that collects, shares, and processes customer information.
As privacy regulation continues to evolve across the United States, dealerships are expected to understand not only what information they collect, but also how it moves across vendors and platforms. The challenge is that many organizations have accumulated technology over several years without periodically reviewing whether every integration remains necessary, accurately disclosed, or appropriately governed.
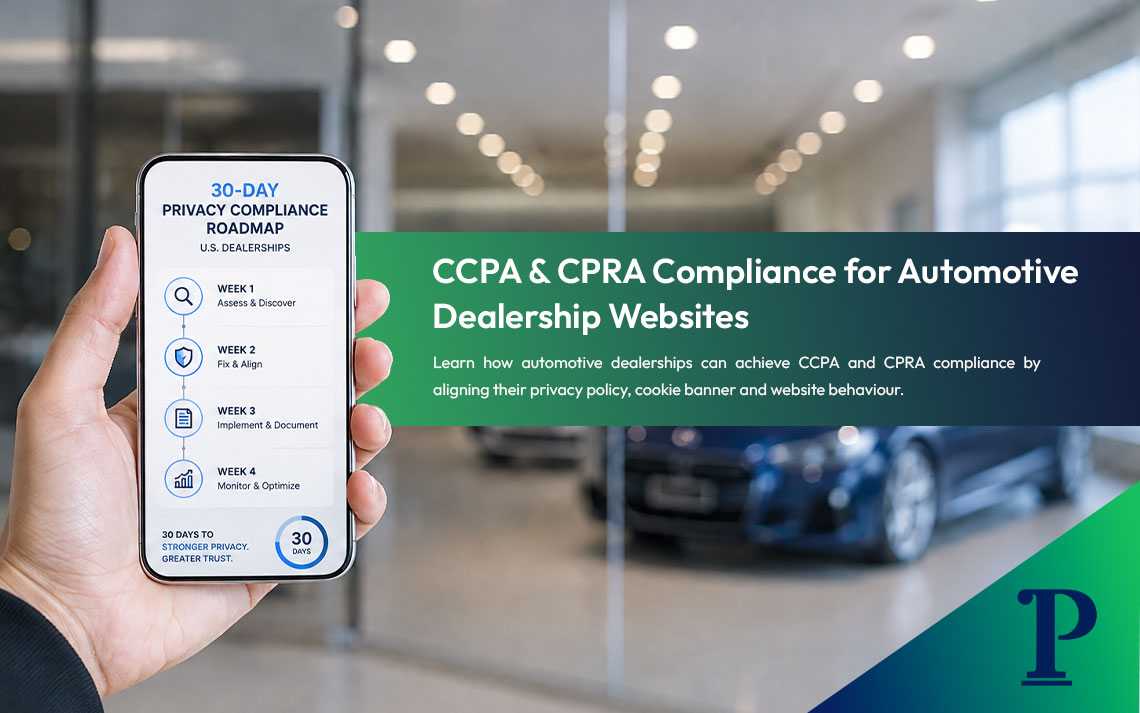
Fortunately, strengthening website privacy does not require rebuilding an entire website. A structured thirty-day roadmap allows organizations to establish visibility, improve governance, and create sustainable processes that reduce regulatory risk while strengthening customer trust.
Week One: Understand Your Current Privacy Landscape
The first week should be dedicated to understanding how the website actually operates. Before updating policies or deploying additional compliance tools, dealerships should develop a clear picture of every technology collecting or transmitting customer information.
A comprehensive website privacy assessment should examine cookies, tracking technologies, analytics platforms, advertising pixels, embedded videos, finance applications, chat providers, inventory widgets, and any third-party scripts running across the website. This exercise frequently uncovers technologies introduced during previous campaigns that continue operating long after their original purpose has ended.
By the end of the first week, the organization should have a documented inventory describing what information is collected, why it is collected, where it is shared, which vendors receive it, and who internally owns each integration. This visibility becomes the foundation for every privacy decision that follows.
Week Two: Align Privacy Notices with Website Behaviour
Once the technical landscape is understood, the next step is ensuring that customer-facing disclosures accurately reflect reality. One of the most common findings during privacy assessments is a disconnect between what a website actually does and what its privacy policy says it does.
Privacy notices should evolve alongside the website. Cookie disclosures, consent mechanisms, consumer rights pages, and form notices should accurately explain the categories of information collected, the purposes for which information is processed, and the choices available to visitors. Consent tools should be tested regularly rather than assumed to function correctly, particularly after website updates or vendor changes.
At the end of this stage, organizations should be confident that the promises made to customers align with the website’s actual technical behaviour.
Week Three: Evaluate Vendors and Data Flows
Customer information rarely remains on the website alone. Data often flows into CRM systems, finance providers, marketing platforms, call-tracking services, OEM technologies, and numerous other vendors. Every integration introduces operational benefits as well as additional privacy responsibilities.
This week should focus on tracing those data flows, reviewing vendor relationships, and confirming that each integration serves a legitimate business purpose. Dealerships should also review their website forms to ensure they collect only the information necessary to complete the customer’s request. Applying data minimization principles reduces operational complexity and lowers privacy risk.
Week Four: Build an Ongoing Governance Program
Privacy compliance is not a one-time project. Websites change continuously as new campaigns launch, technologies evolve, and vendors introduce additional functionality. Sustainable compliance depends on repeatable governance rather than periodic remediation.
Organizations should establish a regular review process covering website assessments, cookie scans, privacy policy updates, consent testing, vendor reviews, and collaboration between marketing, IT, legal, and compliance teams. Privacy becomes significantly more effective when responsibilities are shared across the organization rather than assigned to a single department.
Why This Roadmap Matters
Website privacy is no longer simply a regulatory obligation. It influences customer trust, cybersecurity, operational resilience, and business reputation. Customers increasingly expect transparency about how their personal information is collected and used before they submit a lead form or begin a finance application.
A structured roadmap helps organizations replace uncertainty with visibility. Instead of reacting to complaints or regulatory inquiries, dealerships gain a practical understanding of their digital environment and can make informed decisions about technology, vendors, and customer communications.
How Privacy Pillar Helps
Privacy Pillar partners with automotive dealerships to simplify website privacy compliance through privacy assessments, consent management, vendor reviews, consumer rights workflows, and ongoing governance. Rather than addressing privacy as isolated projects, we help organizations build connected programs that support both regulatory compliance and long-term customer trust.
Final Thoughts
Privacy regulations will continue to evolve, and dealership websites will continue to become more sophisticated. Organizations that regularly assess their websites, maintain accurate disclosures, evaluate vendor relationships, and embed privacy into everyday operations will be better positioned to adapt to future requirements. The first thirty days are not the finish line—they are the starting point for a mature privacy program.
References
1. Federal Trade Commission (FTC) – Protecting Personal Information: A Guide for Business.
2. Federal Trade Commission (FTC) – Automobile Dealers and the FTC’s Safeguards Rule FAQ.
3. National Institute of Standards and Technology (NIST) – Privacy Framework Version 1.0.
4. California Privacy Protection Agency (CPPA) – Consumer Privacy Guidance.
5. National Conference of State Legislatures (NCSL) – Consumer Data Privacy Legislation Tracker. 6. International Association of Privacy Professionals (IAPP) – U.S. State Privacy Law Tracker.